
Pentagon CIO Davies tapped as acting National Cyber Director
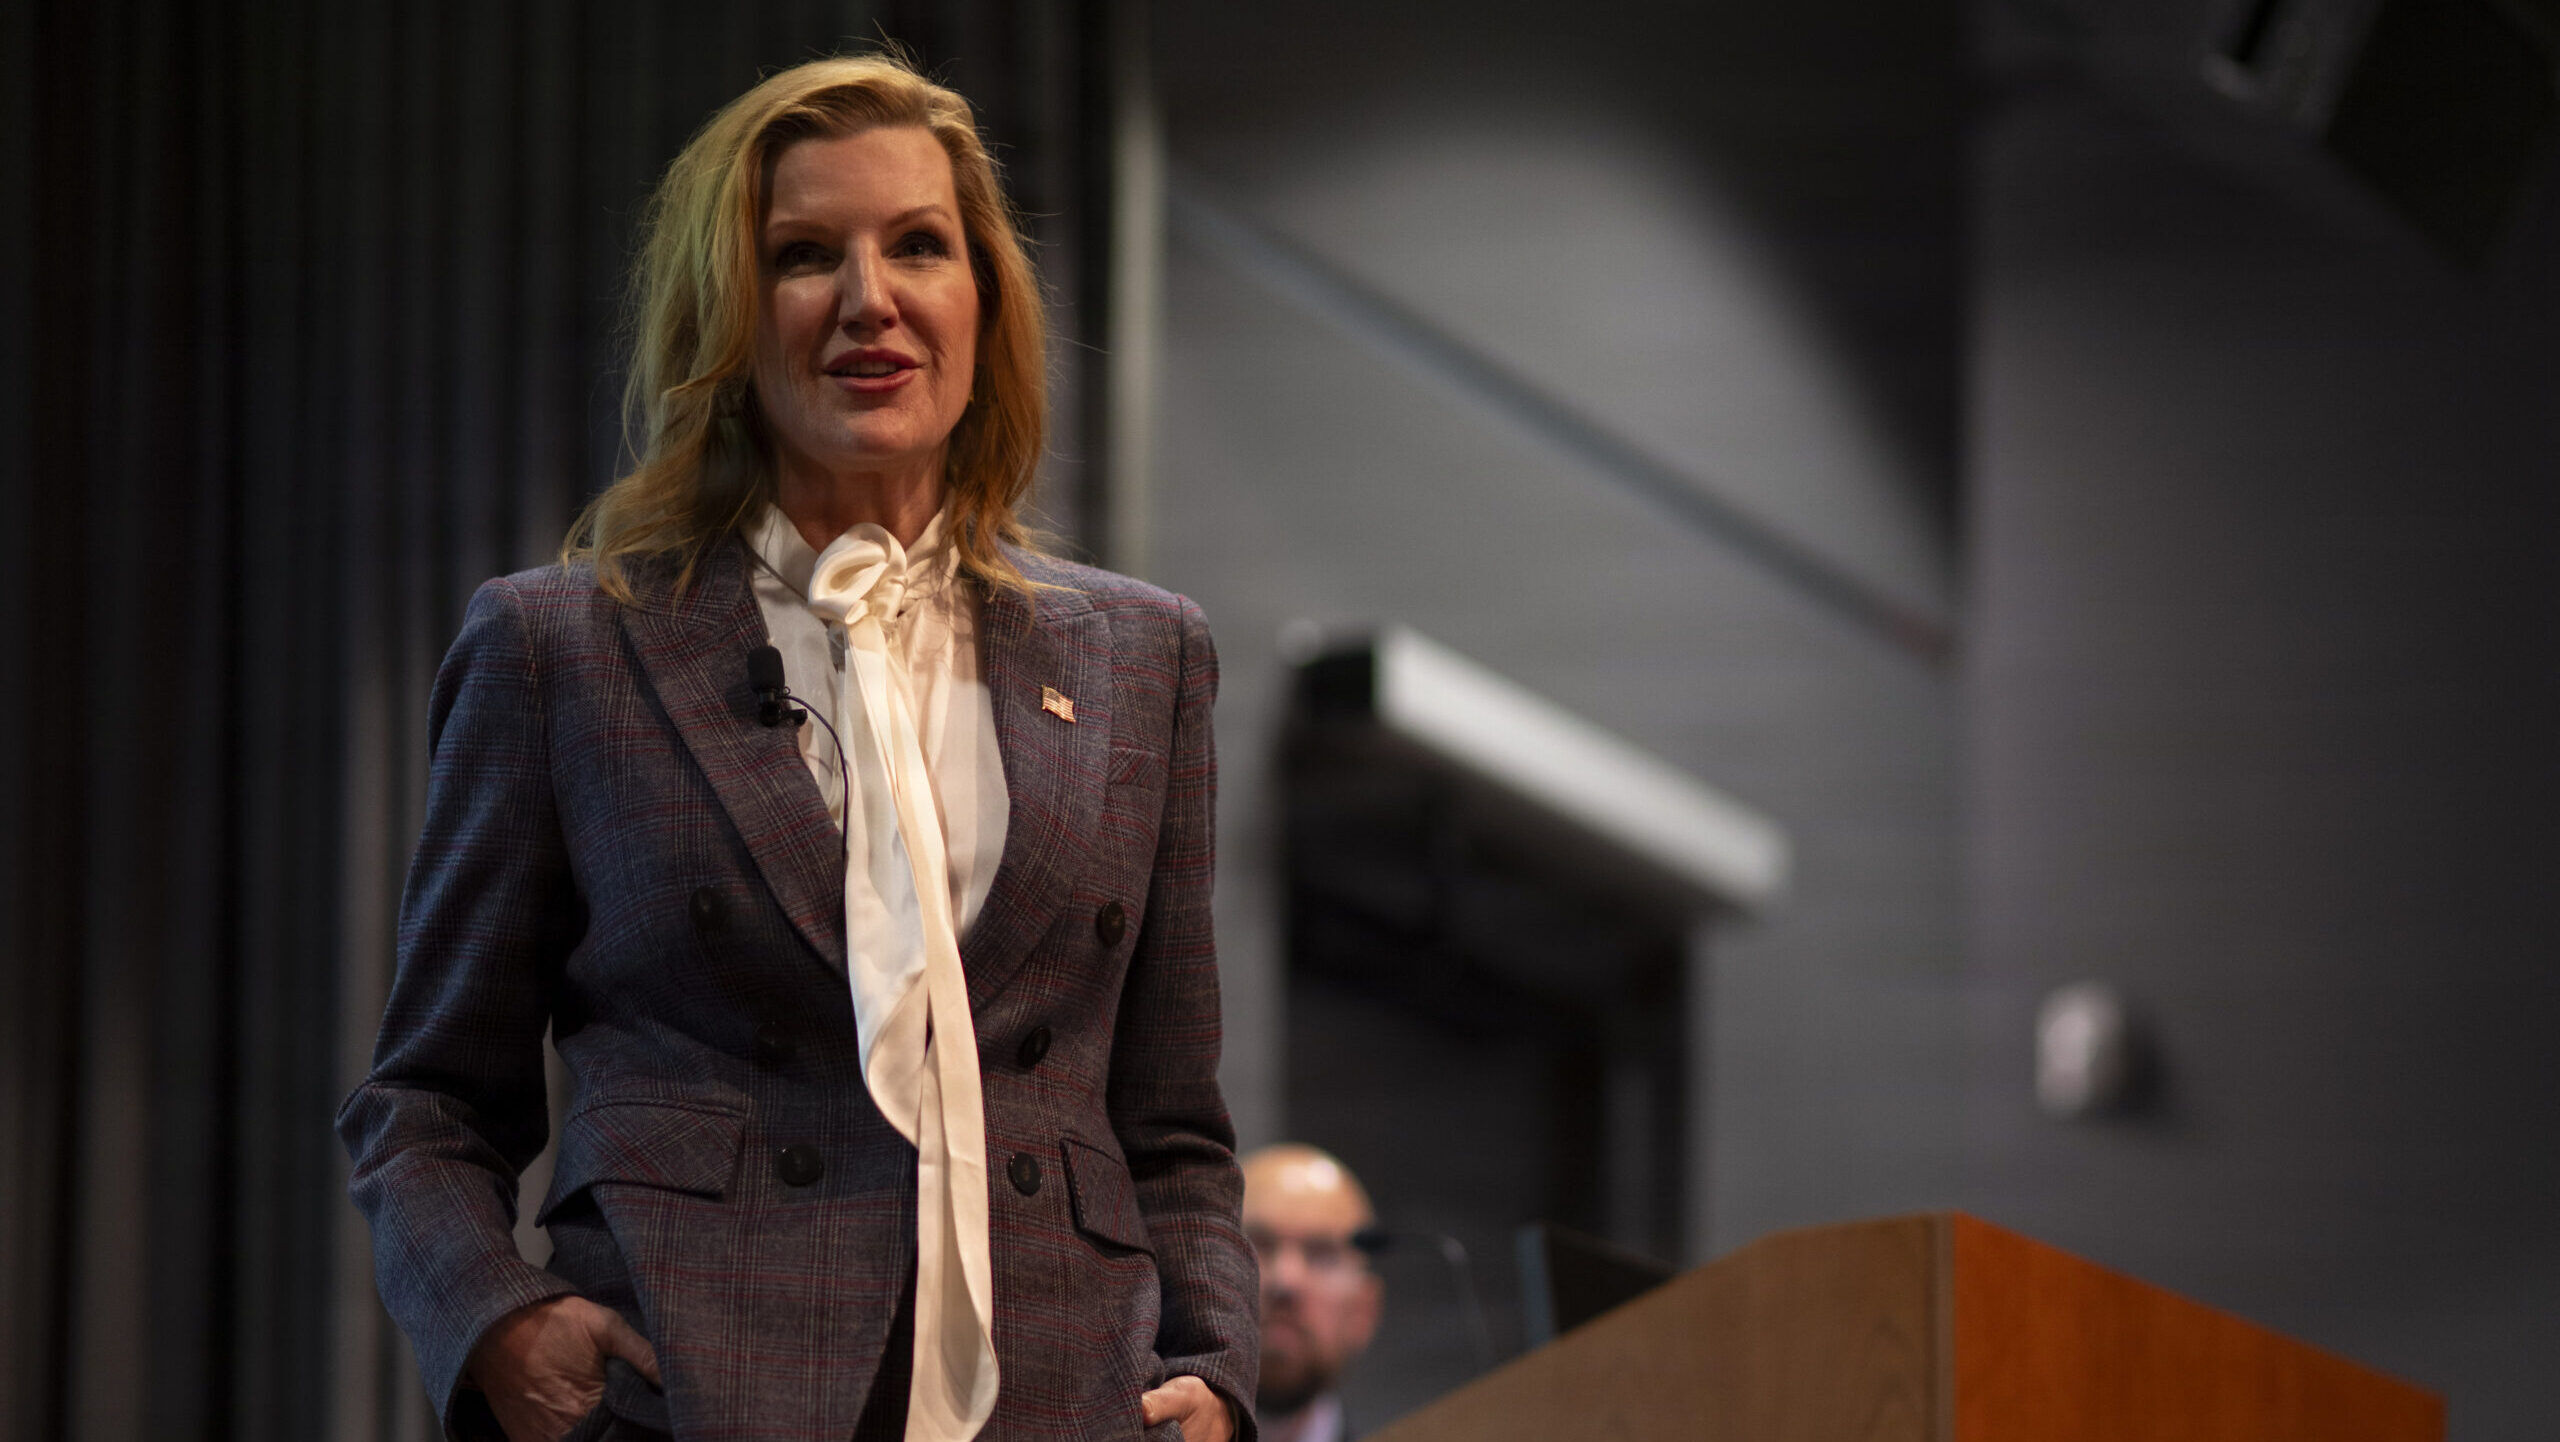
WASHINGTON — Pentagon Chief Information Officer Kirsten Davies has assumed the role of National Cyber Director following the Thursday departure of Sean Cairncross, Secretary of Defense Pete Hegseth confirmed.
Davies also confirmed in a post on X that she would be moving into the White House role, which was created in 2021 to serve as the top advisor to the president on cyber matters and coordinate cyber activities and responses across the myriad government agencies.
“Our nation stands in the crossroad of analog, digital, and quantum technologies, our American way of living increasingly interconnected,” the post, shared from her personal account, reads. “Our opportunity is to dominate the cyber landscape for generations to come …but only if we modernize and drive resilience into the foundations our great nation runs on, as well as build cyber talent for our future.”
It is not clear who is assuming the duties of Pentagon CIO, and the Pentagon did not respond to a request for comment by press time.
Davies takes over at a tense time in which several major cyber and IT incidents have raised alarm bells across the country, with outages ranging from air traffic control to airlines to banks to sensitive national security networks.
Prior to assuming the CIO role in December 2025, Davies served as the chief information security officer at Unilever.
Since taking office, she has stressed four key pillars in the job:
- supporting warfighting systems from IT, operational technology and Internet of Things devices;
- maturing digital capabilities such as speeding the delivery of software and standardizing data architectures;
- transforming cybersecurity; and
- up-skilling and cross-skilling the workforce.
Davies has also inked multiple large contracts under enterprise service agreements. For example, she signed one for Dell in May for $9.7 billion to consolidate Microsoft software, services and licenses across, and one for Oracle in July for $7 billion to consolidate “fragmented, one-off information technology purchases.”
One of the most controversial decisions she has made in her tenure was the suspension of the Cybersecurity Maturity Model Certification’s third-party assessments, which is what some experts refer to as the bedrock of the program. While the initial 60-day review window for the suspension has come and gone, there has not been any update regarding the status of the program or its suspension.